CYBERMINDSPACE’S FLAGSHIP COURSE

COMING SOON

AI Security
Engineering
Course.

Learn to find and fix security risks in AI apps.

Learn with Arun Chaudhary through recorded lessons, hands-on practice and a live mentor class every week.

9 modules1 released each weekAI study support

Coming very soon · Enrollment opens at launch

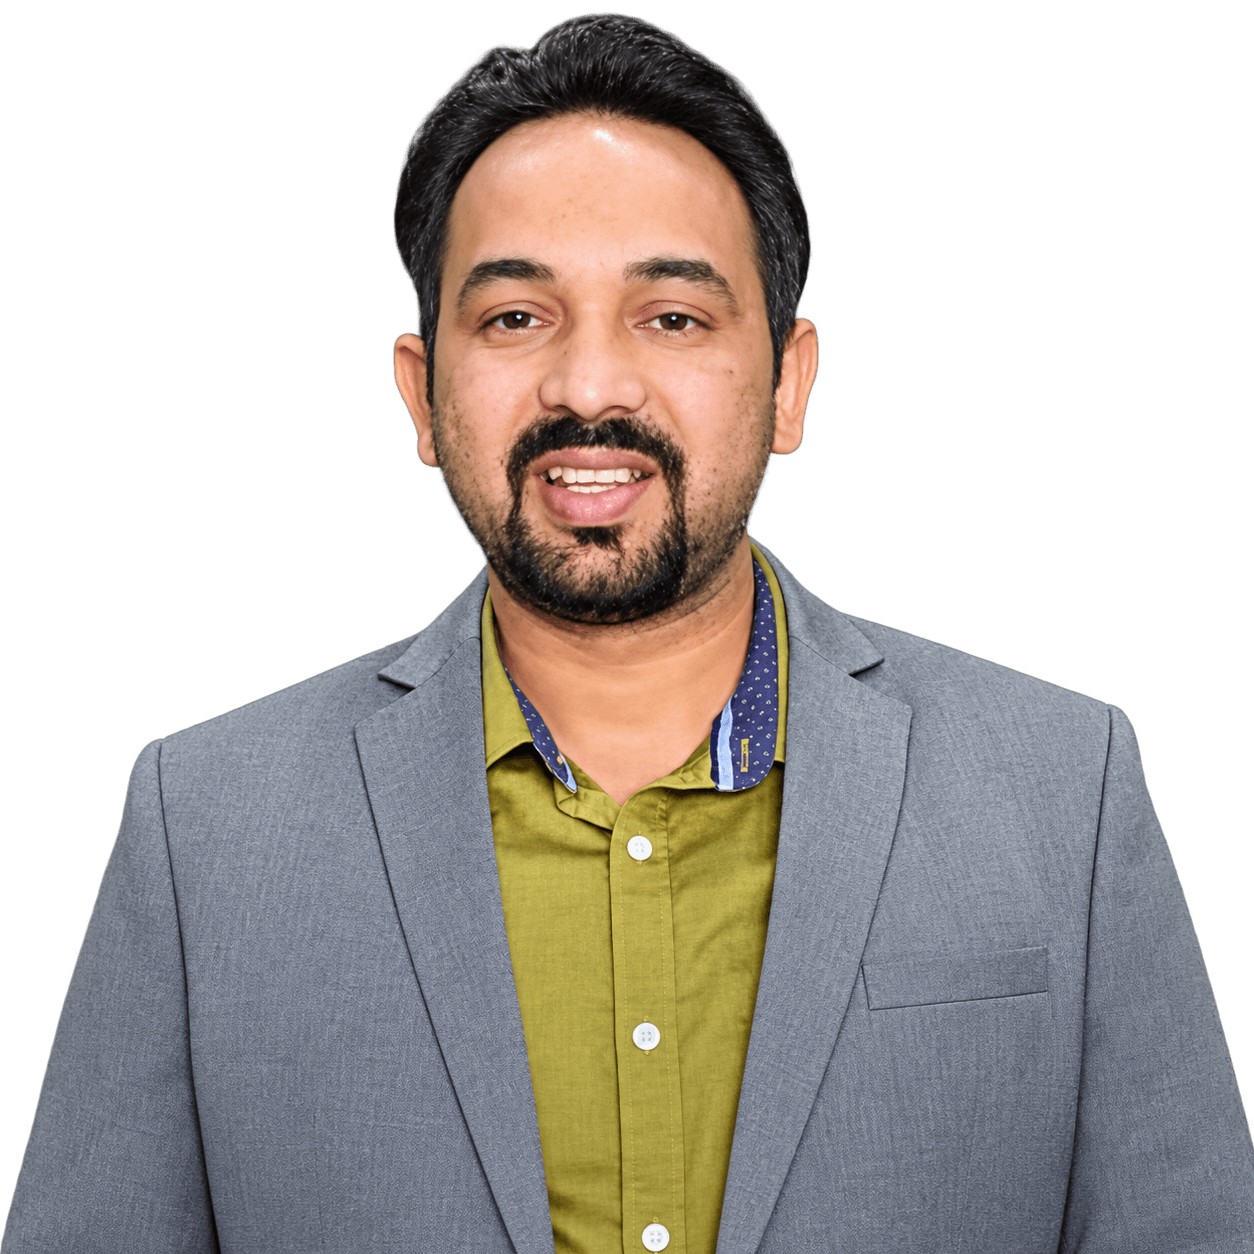
Arun Chaudhary, AI Security Engineering course instructorYOUR COURSE INSTRUCTOR

Arun Chaudhary

Microsoft Certified Trainer

19+ yearsIT experience
2,000+Enterprise training engagements

MORE THAN RECORDED VIDEOS

Learn at your pace.
Get help along the way.

Recorded lessons

Watch and revisit lessons at your own pace.

Weekly live class

Ask questions and learn with a mentor.

AI-powered notes

Review key ideas without starting over.

AI doubt support

Get help with questions while you study.

WHAT THIS COURSE HELPS YOU DO

Build skills you can use
on real AI applications.

From understanding a weakness to testing a fix.

01

Find the risks

Learn how AI chatbots, documents and agents can expose data or take unsafe actions.

02

Test and protect

Practise security tests and learn how to fix the weaknesses you find.

03

Complete an assessment

Put it all together in a final project with findings, fixes and a clear report.

LEARN WITH ARUN CHAUDHARY

Experience that makes
the lessons practical.

Arun brings 19+ years across cloud, cybersecurity and AI, with 2,000+ enterprise training engagements.

Read Arun’s full profile
  • Microsoft Top 100 Award-Winning Instructor
  • Microsoft Certified Trainer (MCT)
  • EC-Council Authorized Instructor
  • CompTIA authorized trainer

YOUR COURSE CURRICULUM

9 modules.
One new module every week.

Start with the basics of AI security. Finish with a full assessment. Expand any module for the detailed syllabus.

WEEK 01

AI Security Foundations & Threat Modeling

Understand how AI systems work and where security risks begin.

Concepts

  • AI security vs conventional application security.
  • Generative AI, LLM applications, RAG systems and agentic applications.
  • AI application layers: model, application, data, retrieval, tools, identity and runtime.
  • AI-specific trust boundaries and attack surfaces.
  • Assets, sensitive data, identities, privileges and high-impact actions.
  • Threat actors, abuse cases, attack paths and business impact.
  • AI security requirements and threat modeling.
  • Current OWASP LLM/GenAI and Agentic AI risk landscape.
  • AI risk lifecycle: discover, assess, mitigate, monitor and improve.

Hands-on practice

  • Map a reference enterprise AI assistant from user -> application -> LLM -> RAG/tools -> data.
  • Identify trust boundaries, sensitive assets, identities and privileged actions.
  • Create a threat model for LLM, RAG and agent components.
  • Prioritize the top attack paths by likelihood and impact.
  • Convert the threat model into an initial AI security test plan.
WEEK 02

LLM Security

Find data leaks and unsafe behaviour in AI chatbots.

Concepts

  • LLM interaction model: system, developer and user instructions.
  • Context windows, conversation history and memory.
  • Instruction hierarchy and trust boundaries.
  • Sensitive information disclosure and data exposure.
  • System prompt leakage.
  • Secrets in prompts, context and logs.
  • Improper output handling and downstream injection.
  • Model output as untrusted data.
  • Misinformation, reliability and confidence limitations.
  • Unbounded consumption and abuse controls.

Hands-on practice

  • Trace input -> context -> model -> output in a controlled LLM application.
  • Test system-prompt leakage and sensitive-information disclosure.
  • Identify secrets and sensitive content entering the model context.
  • Trace unsafe model output into a downstream application consumer.
  • Implement output validation/encoding and retest.
  • Create repeatable LLM security regression cases.
WEEK 03

Prompt Injection & LLM Application Security

Learn how malicious instructions can trick an AI application.

Concepts

  • Direct prompt injection.
  • Indirect prompt injection.
  • Instruction conflicts and context manipulation.
  • Untrusted content and trust-boundary violations.
  • System-prompt extraction and instruction override attempts.
  • Injection through files, webpages, retrieval results and external content.
  • Prompt injection against tool-enabled applications.
  • Isolation, validation, authorization and policy enforcement.
  • Why prompt secrecy is not a security boundary.
  • Security boundaries around model inputs, context and actions.

Hands-on practice

  • Attack a deliberately vulnerable chatbot with controlled direct injection cases.
  • Introduce malicious instructions through untrusted documents/web content.
  • Identify the exact trust boundary that failed.
  • Test whether injected instructions can influence downstream actions.
  • Apply isolation, deterministic validation, authorization and tool restrictions.
  • Retest the original attacks and compare security before/after controls.
WEEK 04

RAG Security

Protect the documents and data your AI uses to answer questions.

Concepts

  • RAG pipeline: ingestion -> chunking -> embedding -> vector storage -> retrieval -> context -> generation.
  • Embedding and vector-database security.
  • Retrieval attack surface.
  • Unauthorized retrieval and sensitive-data leakage.
  • Document-level and tenant-level authorization.
  • Data poisoning and malicious documents.
  • Retrieval manipulation.
  • Indirect prompt injection through retrieved content.
  • Metadata/filter security.
  • Why vector similarity is not authorization.
  • Identity-aware retrieval and data isolation.

Hands-on practice

  • Map a deliberately vulnerable RAG pipeline.
  • Insert controlled poisoned/malicious documents and observe retrieval behavior.
  • Test unauthorized and cross-user document retrieval.
  • Test indirect prompt injection through retrieved content.
  • Evaluate metadata, filtering and embedding/retrieval weaknesses.
  • Implement identity-aware retrieval and document-level authorization.
  • Retest leakage, poisoning and authorization scenarios.
WEEK 05

AI Agent Security & Tool Abuse

Secure AI agents that use tools, files and external services.

Concepts

  • Agent architecture and agentic workflows.
  • Planning, execution loops and agent memory.
  • Tool/function calling and external integrations.
  • Agent identity and service identities.
  • Tool authorization and permission boundaries.
  • Agent goal hijacking.
  • Tool misuse and exploitation.
  • Identity and privilege abuse.
  • Memory/context poisoning.
  • Excessive agency and unsafe autonomy.
  • Human approval gates.
  • Least privilege, sandboxing and runtime containment.
  • MCP/tool integration security.
  • Inter-agent communication and trust boundaries.

Hands-on practice

  • Audit an agent with database, file, email and API tools.
  • Identify excessive permissions and dangerous tool combinations.
  • Execute controlled agent goal-hijacking and tool-misuse scenarios.
  • Trace user input -> model -> tool -> external system.
  • Redesign permissions using least privilege.
  • Add authorization and human approval for high-impact actions.
  • Assess a sandboxed MCP/third-party tool integration.
  • Retest the original attack paths.
WEEK 06

AI Application, Supply Chain & Runtime Security

Check the models, dependencies and settings behind an AI application.

Concepts

  • AI application attack surface beyond the prompt layer.
  • Third-party models, libraries, packages and AI components.
  • Model provenance and component integrity.
  • Data and model poisoning.
  • Embedding/retrieval data integrity.
  • Secrets, API credentials and configuration security.
  • Deployment isolation and environment separation.
  • AI component inventory and provenance.
  • Runtime abuse and resource controls.
  • Operational monitoring and suspicious-behavior signals.

Hands-on practice

  • Analyze a controlled AI supply-chain scenario and identify untrusted components.
  • Inspect model/data provenance and dependency risks.
  • Locate secrets and unsafe configuration in a sample AI deployment.
  • Analyze a poisoned-data scenario and identify the integrity failure point.
  • Define runtime controls for resource abuse and suspicious behavior.
  • Create a prioritized supply-chain and runtime remediation plan.
WEEK 07

AI Red Teaming, Security Testing & Evaluation

Run repeatable tests and turn weaknesses into clear findings.

Concepts

  • AI red teaming vs conventional application penetration testing.
  • Authorized scope, test boundaries and assessment planning.
  • Attack-surface discovery and adversarial test design.
  • Prompt-injection, disclosure, RAG and agent/tool test categories.
  • Finding validation and reproducibility.
  • Evidence collection and attack-path analysis.
  • Risk/severity and business-impact reasoning.
  • Security evaluation datasets and regression suites.
  • Attack success rate and other practical security metrics.
  • False positives/false negatives in AI security testing.
  • Automated security regression testing.
  • Retesting, residual risk and continuous evaluation.
  • Test coverage and regression management.

Hands-on practice

  • Build an AI security test plan from a supplied application architecture.
  • Create a reusable attack suite covering LLM, RAG and agent risks.
  • Execute attacks and capture reproducible evidence.
  • Separate suspected weaknesses from validated vulnerabilities.
  • Build a small automated security regression suite.
  • Run the suite against two application/control versions.
  • Measure which attacks succeed/fail and investigate regressions.
  • Write professional findings with root cause, impact, remediation and retest criteria.
WEEK 08

AI Security Engineering, Runtime Defense & Incident Response

Build defenses, monitor attacks and respond to incidents.

Concepts

  • Secure AI architecture patterns.
  • Defense in depth.
  • Identity-aware data access.
  • Instruction/data separation.
  • Input controls and output validation.
  • Retrieval authorization.
  • Tool authorization and action boundaries.
  • Isolation and sandboxing.
  • Monitoring, telemetry and abuse detection.
  • Rate limits and resource controls.
  • Human approval for consequential actions.
  • Runtime containment.
  • AI security incident indicators and evidence sources.
  • AI incident triage, containment, rollback and recovery.
  • Post-incident retesting and lessons learned.

Hands-on practice

  • Design a secure reference architecture for an enterprise AI assistant.
  • Map major vulnerabilities to preventive and detective controls.
  • Design controls for input, output, retrieval and tool execution.
  • Define telemetry for prompt injection, retrieval abuse and tool misuse.
  • Investigate a simulated AI security incident using application/agent traces.
  • Contain the affected capability, preserve evidence and restore a safe state.
  • Perform a control-gap analysis and define the final retest plan.
WEEK 09

Capstone - End-to-End AI Security Assessment

Bring your skills together in a complete AI security assessment.

Concepts

  • Enterprise AI assistant with LLM + RAG + agent/tool layer.
  • Application and data-flow discovery.
  • Threat modeling.
  • Risk-based testing.
  • Finding validation and evidence.
  • Security-control design.
  • Security evaluation and regression testing.
  • Incident-response scenario.
  • Retesting and residual risk.
  • Technical and executive reporting.

Hands-on practice

  • Phase 1 - Discover: map architecture, identities, data, RAG and tools.
  • Phase 2 - Threat model: identify trust boundaries and attack paths.
  • Phase 3 - Attack: test prompt injection, disclosure, RAG authorization/poisoning and agent/tool abuse.
  • Phase 4 - Validate: reproduce and document findings.
  • Phase 5 - Defend: apply or specify mitigations.
  • Phase 6 - Evaluate: run the security regression suite.
  • Phase 7 - Respond: investigate a simulated AI security incident and contain it.
  • Phase 8 - Retest and report: deliver technical findings, executive summary and remediation roadmap.

IS IT FOR YOU?

For people ready to learn AI security.

DevelopersLearn to secure the AI applications you build.

Security professionalsAdd AI testing and defense to your skills.

Cybersecurity learnersBuild on your basics with a structured course.

Basic knowledge of applications, APIs and security will help you get more from the course.

YOUR QUESTIONS, ANSWERED

Before you join.

When can I join?

The course is coming very soon. Enrollment and pricing are not announced yet. Contact our course team to ask about launch details.

Is it recorded or live?

You get recorded course lectures plus one live class with a mentor each week. Class timings will be announced at launch.

Will I get all nine modules at once?

One module launches each week after the course begins, across nine weeks. Each module builds on the previous one.

Is this course right for me?

It is designed for developers, cybersecurity learners and professionals interested in securing AI applications. Basic knowledge of applications, APIs and cybersecurity will help. The first module covers AI security foundations.

How will I get help?

Use the AI notes and doubt solvers while studying, and bring deeper questions to your weekly live mentor class. AI answers should be checked through practice and mentor guidance.

COMING VERY SOON

Interested in the course?
Let’s talk.

Ask our course team about the launch, enrollment or whether the course is right for you.

No payment required to enquire.

Talk to the course team

AI Security Engineering
with Arun Chaudhary

Email your course enquiry+91 70118 33373The email button opens a ready-to-edit message in your email app. Send it to reach our team.
AI Security EngineeringComing very soon
Enquire